> ## Documentation Index
> Fetch the complete documentation index at: https://docs.gcore.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Settings for one hostname
> When a setting applies to a whole CDN hostname, and when a rule overrides it for a matching path.
**OPTIONS** applies to every request for the hostname. **RULES** overrides that behavior where the URI matches a path or a regular expression, and only for the options placed on the rule. Anything the rule does not mention stays as set under **OPTIONS**.
## OPTIONS
### General
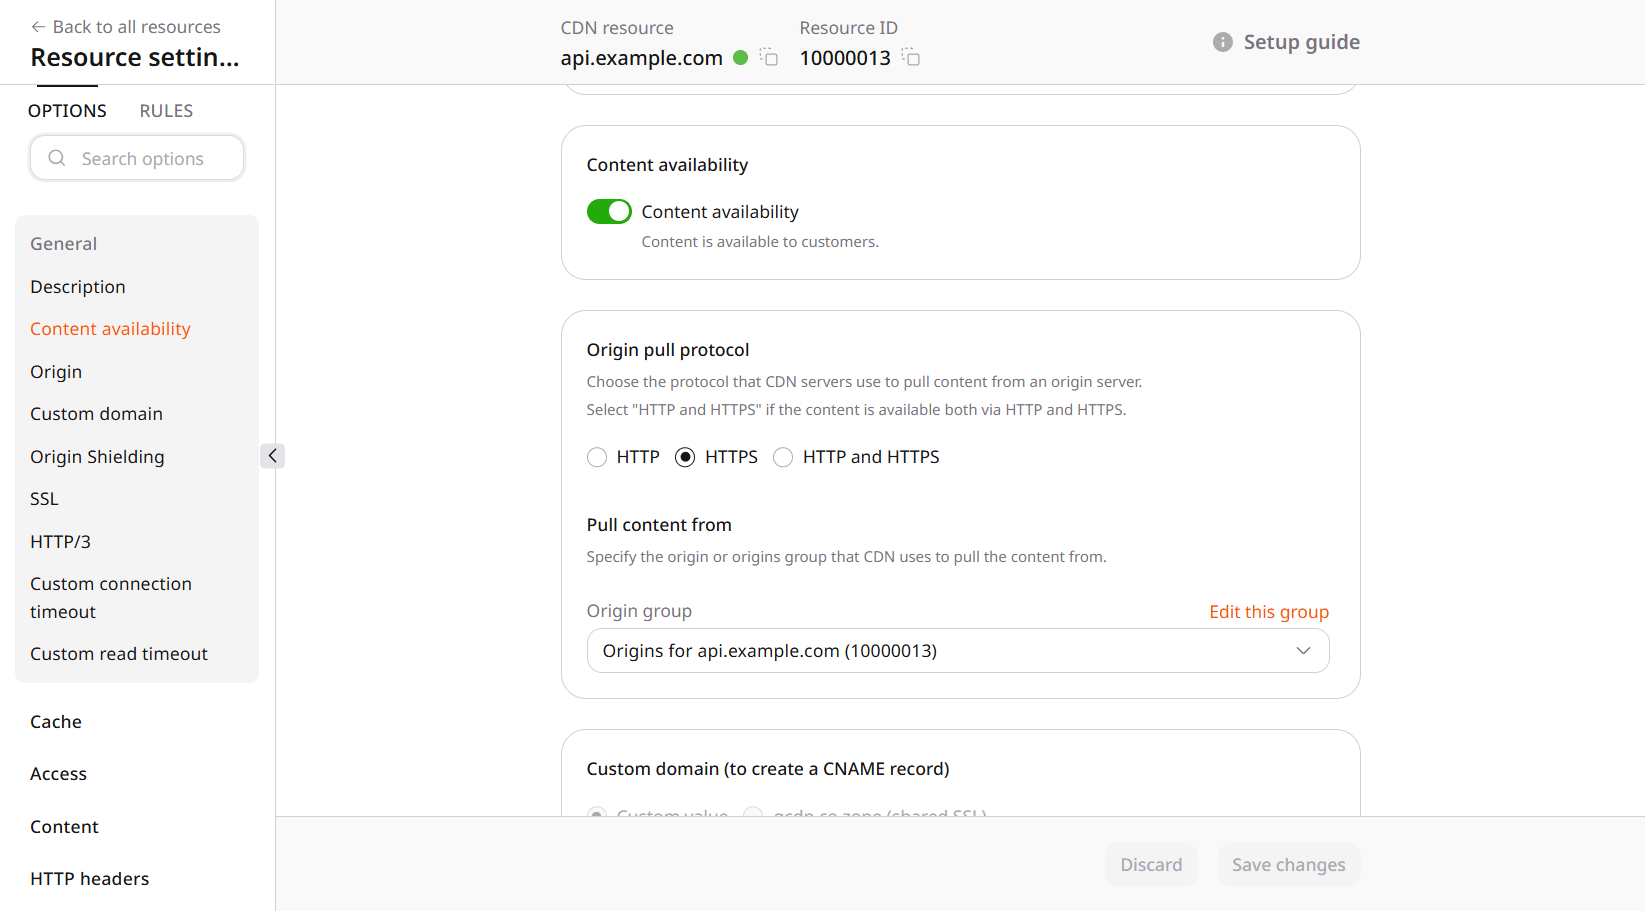
Files are pulled from an origin group. [Origin pull](/cdn/cdn-resource-options/general/specify-an-origin-and-the-origin-pull-protocol) sets the protocol to HTTP, HTTPS, or both, and selects the group. The sources in the group are edited in [origin groups](/reseller-support/cdn/origin-groups).
 To keep every edge from calling that origin, [Origin Shielding](/cdn/cdn-resource-options/general/enable-and-configure-origin-shielding) places one precache server in front of it. A hit is served from the shield, and the origin is contacted on a miss. Brotli, under Content, has no effect until the shield is enabled.
[Connection timeouts](/cdn/cdn-resource-options/general/customize-connection-and-read-timeouts) limit how long an edge waits to open a connection to the origin, and how long it waits for the next bytes of the response.
**Content availability** is the switch for delivery. While it is on, content is available to customers. The name viewers request is fixed after the resource is created: a [custom domain](/cdn/cdn-resource-options/general/create-and-set-a-custom-domain-for-the-content-delivery-via-cdn), or a name in the gcdn.co zone. They reach it with a [Let's Encrypt](/cdn/ssl-certificates/configure-a-lets-encrypt-certificate) certificate, which renews automatically, or with a [custom certificate](/cdn/ssl-certificates/configure-your-own-ssl-certificate). **HTTP/3** applies only while HTTPS is on. [DNS-01](/cdn/ssl-certificates/use-dns-01-for-a-lets-encrypt-certificate) matters only when the HTTP challenge cannot reach the hostname.
### Cache
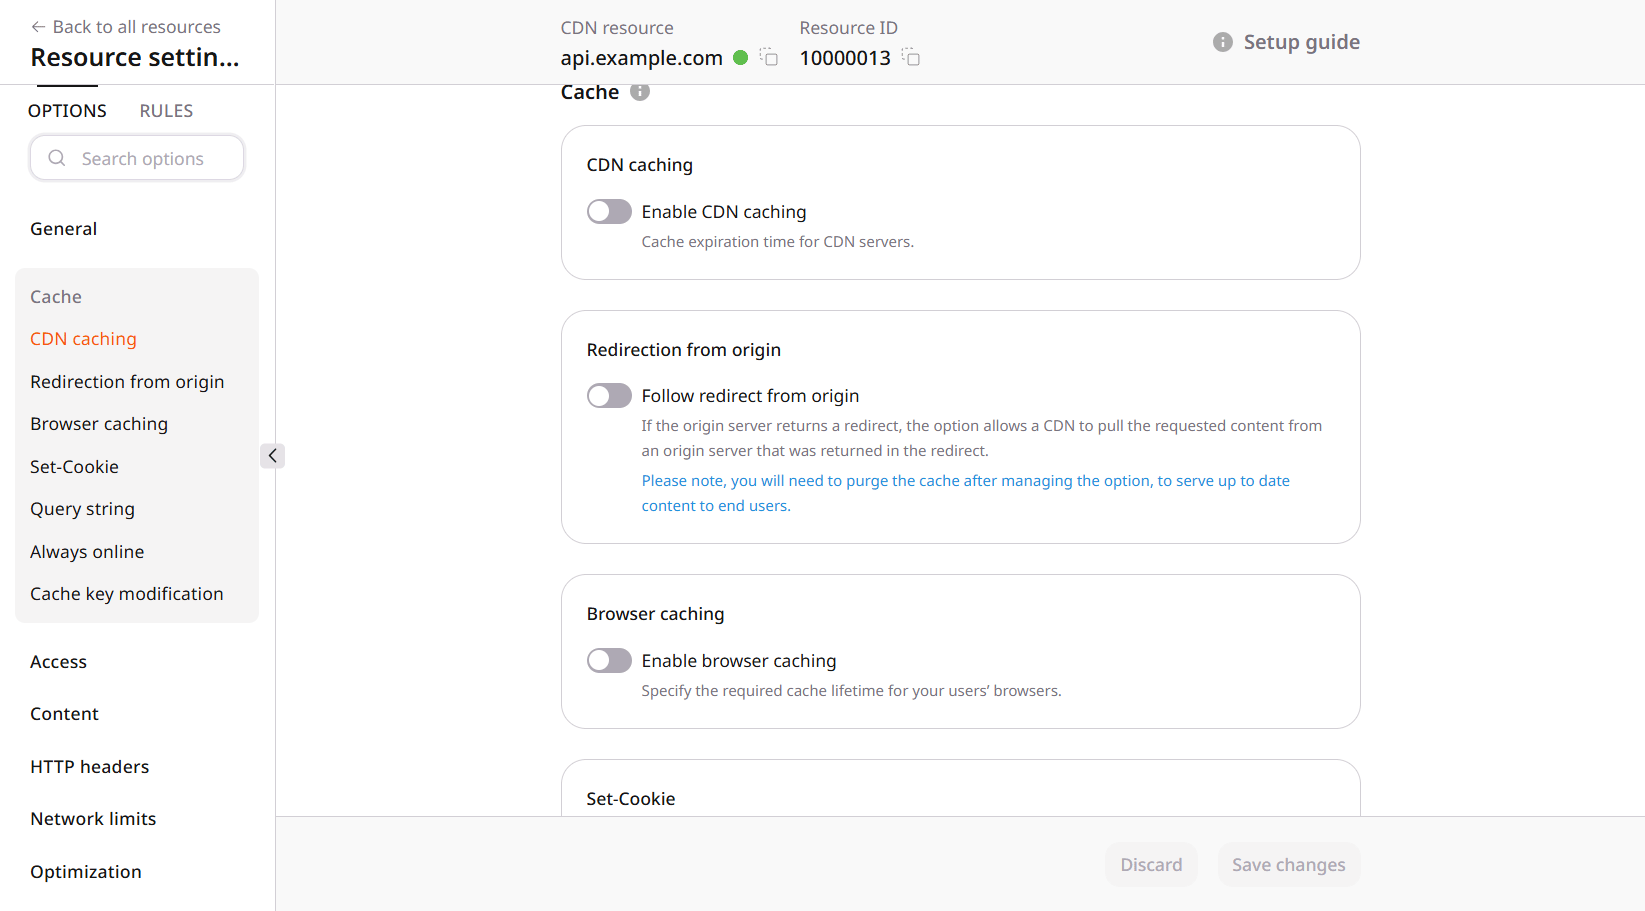
[CDN caching](/cdn/cdn-resource-options/cache/specify-cache-lifetime-on-a-cdn-resource-or-origin) is the edge lifetime. [Browser caching](/cdn/cdn-resource-options/cache/specify-cache-lifetime-for-user-browsers) is the lifetime in the viewer's browser. Changing one leaves the other as it was. A different lifetime for one path belongs on a rule.
 The same file with a different query string, or with a `Set-Cookie` header, can be stored once or many times. Ignoring the [query string](/cdn/cdn-resource-options/cache/ignore-the-set-cookie-or-query-string-parameters-when-caching-content-on-cdn-servers) or [Set-Cookie](/cdn/cdn-resource-options/cache/ignore-the-set-cookie-or-query-string-parameters-when-caching-content-on-cdn-servers) keeps one object. The [cache key](/cdn/cdn-resource-options/cache/modify-cache-key) names the request parts that must be stored apart, and changing that key drops the copies already stored.
A redirect from the origin is stored and returned as a redirect. [Origin redirects](/cdn/cdn-resource-options/cache/set-up-a-cdn-resource-to-follow-origin-redirects) follow the selected codes and store the target instead. When the origin cannot return a fresh object, [Always online](/cdn/cdn-resource-options/cache/always-online-provide-the-stale-cache-if-the-origin-is-unavailable) can serve one that is already cached.
### Access
[Access policies](/cdn/cdn-resource-options/security/control-access-to-the-content-with-country-referrer-ip-and-user-agents-policies) filter by country, referrer, IP address, or user agent. **Allow by default** rejects only the listed values. **Block by default** accepts only those values. A [secure token](/cdn/cdn-resource-options/security/use-a-secure-token/about-secure-token) goes further and ties the URL to a time limit or to an allowed IP address.
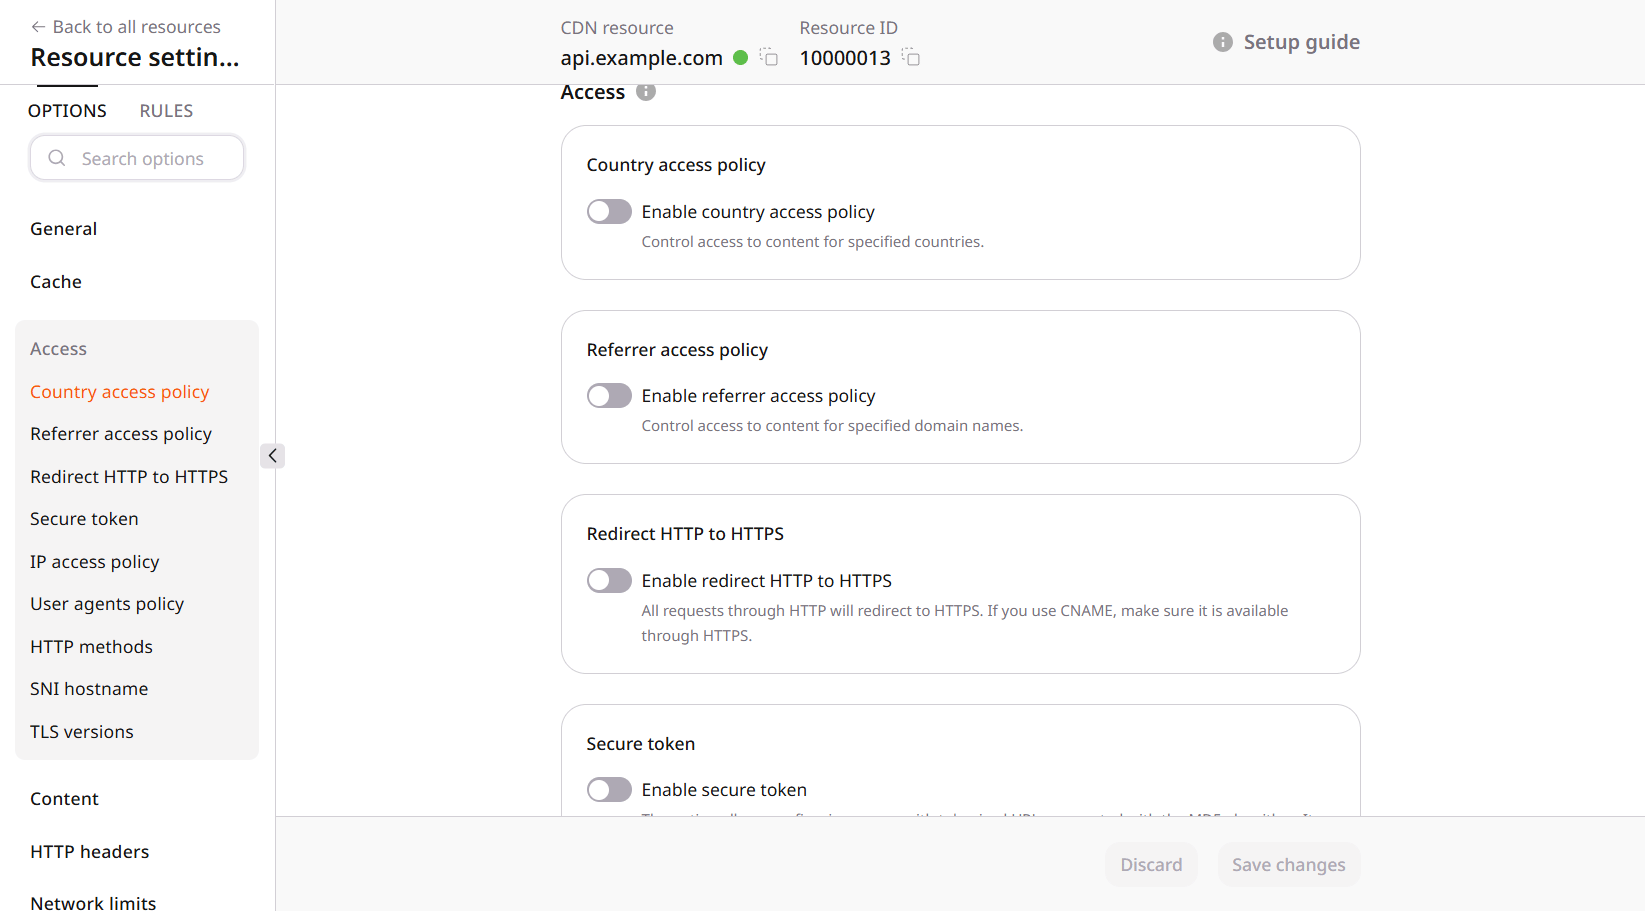 HTTP requests can follow an [HTTPS redirect](/cdn/cdn-resource-options/security/set-up-a-redirect-from-http-to-https). Methods the hostname should not serve are limited under [HTTP methods](/cdn/cdn-resource-options/security/specify-http-methods-allowed-for-content-requests-from-the-cdn).
[SNI hostname](/cdn/cdn-resource-options/security/set-the-hostname-passed-in-sni-requests-to-the-origin-server) and [TLS versions](/cdn/cdn-resource-options/security/choose-tls-versions) sit together and apply to different ends of the path. SNI is the name sent to the origin during its handshake, and only when the pull uses HTTPS. **Dynamic** follows the Host header. **Custom** sends a name set for the origin. TLS versions limit what a viewer may use to reach the hostname.
### Content
A [status code](/cdn/cdn-resource-options/specify-custom-http-status-code-for-the-content-delivered-by-the-cdn) can replace the origin response for every request. The same replacement for one path is a rule.
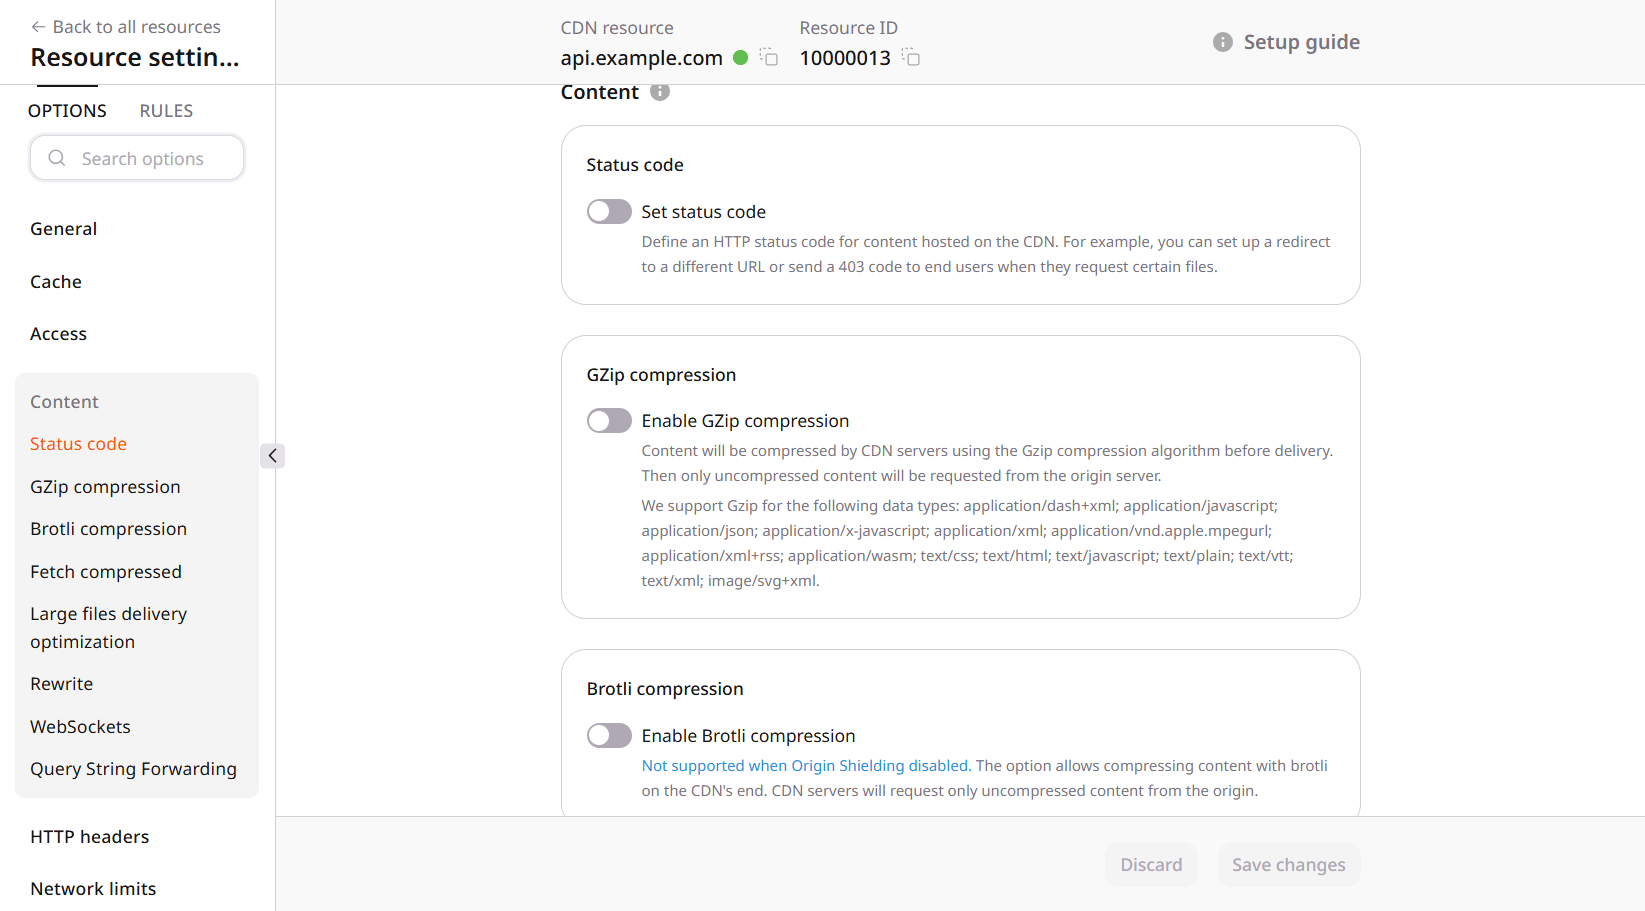 Uncompressed text can be compressed at the edge. [Edge compression](/cdn/cdn-resource-options/compression/configure-gzip-and-brotli-compression) does that with Gzip or Brotli, and Brotli requires Origin Shielding.
On the resource, or inside one rule, that compression cannot run together with [Fetch compressed](/cdn/cdn-resource-options/compression/configure-fetch-compression), which pulls files the origin already compressed, or with [large files](/cdn/cdn-resource-options/optimize-large-file-delivery), which delivers big objects in parts.
The path the origin sees can differ from the path the viewer used. [Rewrite](/cdn/cdn-resource-options/rewrite-redirect-requests-from-the-cdn-to-the-origin) changes it before the fetch, or returns a redirect.
[WebSockets](/cdn/cdn-resource-options/websockets-allow-permanent-connections-with-the-origin) proxy an open connection to the origin.
A token on a playlist does not reach the files inside it on its own. [Query forwarding](/cdn/cdn-resource-options/query-string-forwarding) copies the query parameters onto those URLs.
### HTTP headers
On the way to the origin, the CDN can add [request headers](/cdn/cdn-resource-options/http-headers/specify-http-headers-that-cdn-adds-to-requests-to-the-origin) and can set which site a shared server should answer. That site is the [host header](/cdn/cdn-resource-options/http-headers/configure-and-check-the-host-header): the hostname the viewer requested, or one fixed value on every origin request.
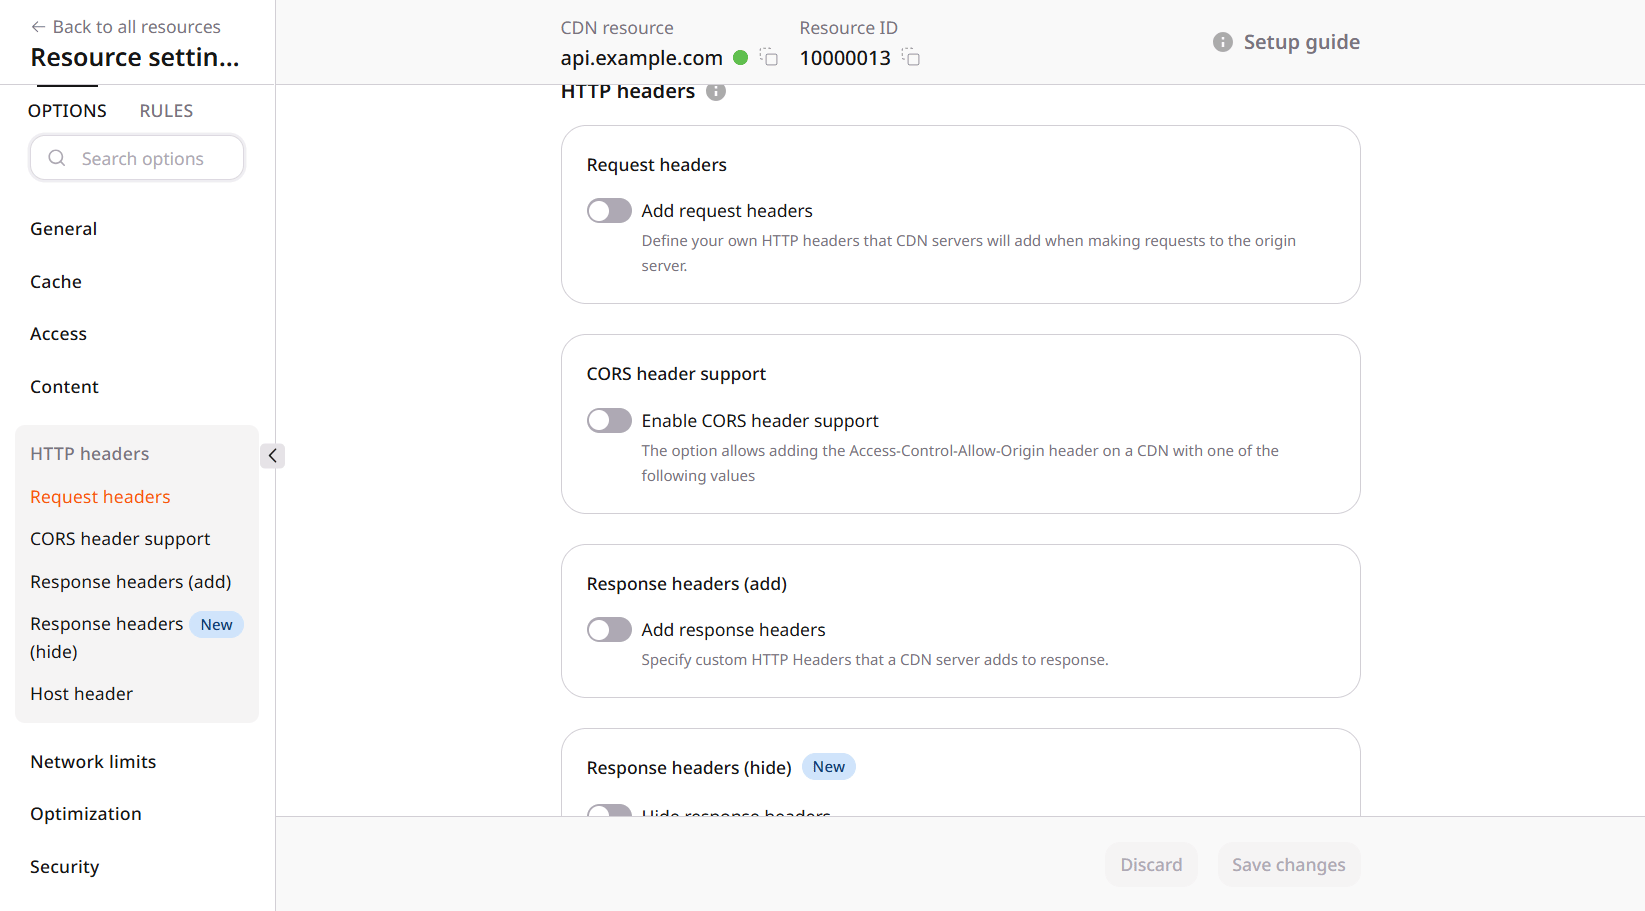 The response back to the viewer is a separate edit. A [CORS header](/cdn/cdn-resource-options/http-headers/add-the-access-control-allow-origin-header-to-the-browser-response) lets the browser accept the response from this hostname. [Response headers](/cdn/cdn-resource-options/http-headers/add-or-hide-response-headers) can be added on that response, or hidden when the origin sent them.
### Network limits
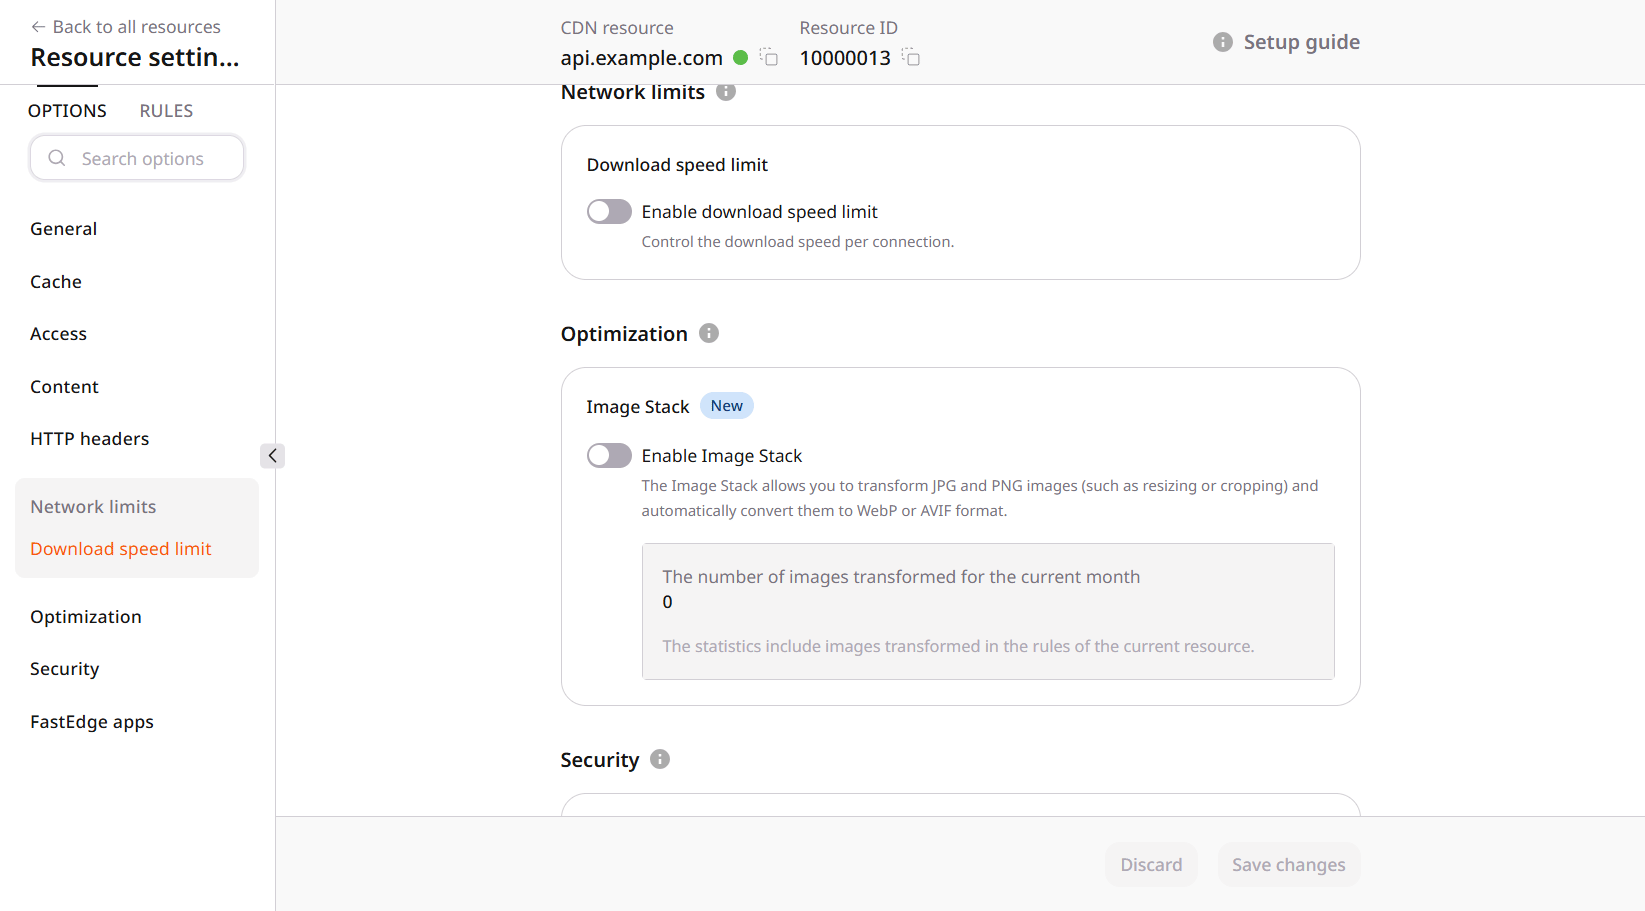
A large file can occupy a connection for the whole transfer. [Download speed](/cdn/cdn-resource-options/network-limits-set-the-content-delivery-speed-to-end-users) holds each connection to a lower rate, either one rate for every connection or a rate taken from the request.
 ### Optimization
[Image Stack](/cdn/cdn-resource-options/image-optimization-paid/about-image-stack) can change the quality, format, or size of a JPG or PNG on the way to the viewer. The file on the origin stays as it was. Enabling it for every request conflicts with Rewrite when the origin also serves other files. A rule can limit the processing to image paths.
 ### Security
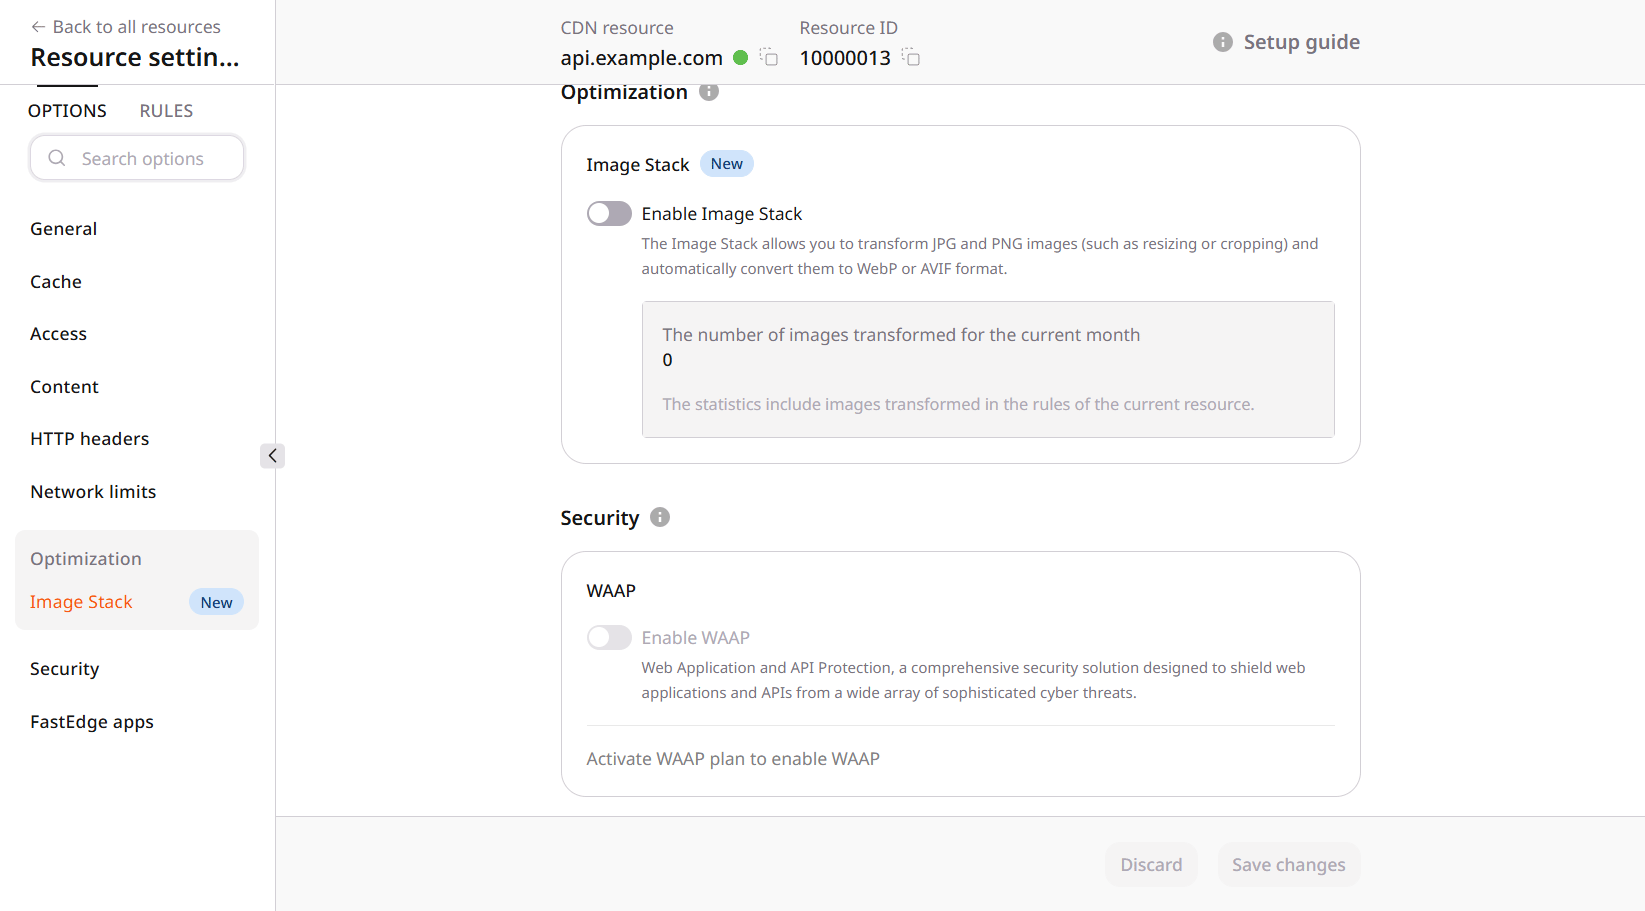
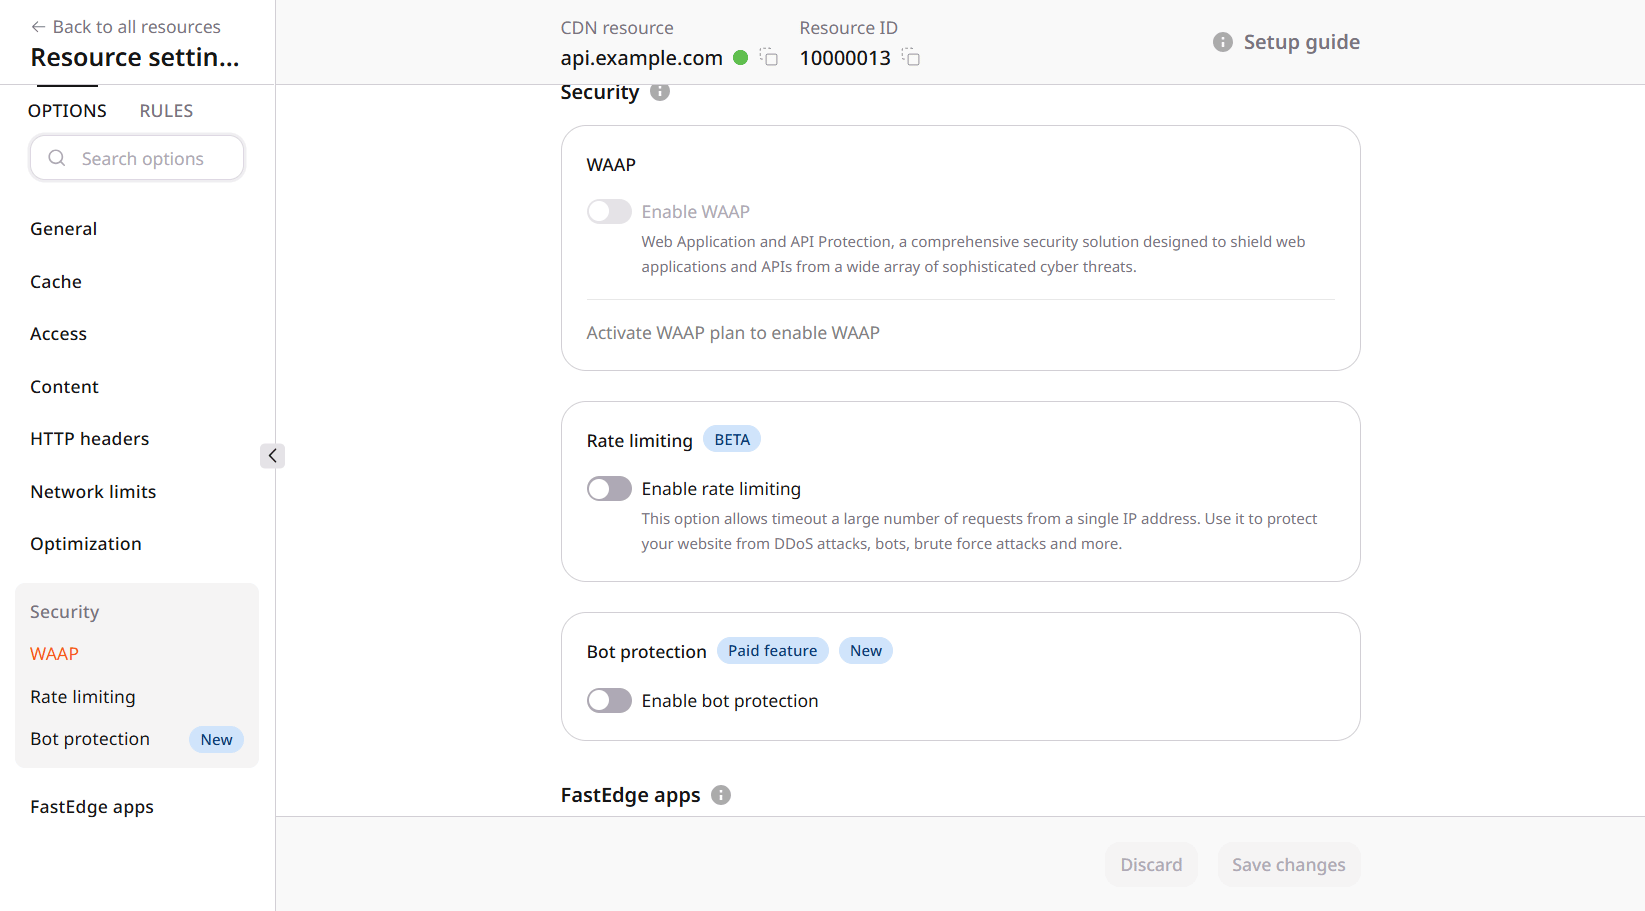
[WAAP](/cdn/cdn-resource-options/cdn-security/protect-cdn-resources-with-waap) inspects requests and can block malicious ones before they reach the origin. The switch stays disabled until a WAAP plan is active. **Rate limiting**, marked **BETA**, only caps how many requests one IP address can send. **Bot protection** is a paid control on the same form.
 ### FastEdge apps
[FastEdge applications](/cdn/getting-started/integrate-cdn-with-fastedge) run during CDN processing and can change the request or the response. Each stage of that processing accepts one application.
 ## RULES
A path that should not follow the resource settings needs a rule. The rule matches a URI path or a regular expression, and its pull protocol can stay inherited or be set to HTTP, HTTPS, or both. When several rules match one URI, the rule listed first applies.
| On the rule | For a matching request |
| - | - |
| The option is absent | The resource setting stays in effect |
| The option is present and disabled | That resource setting is turned off |
| The option is present and enabled | The value on the rule replaces the resource setting |
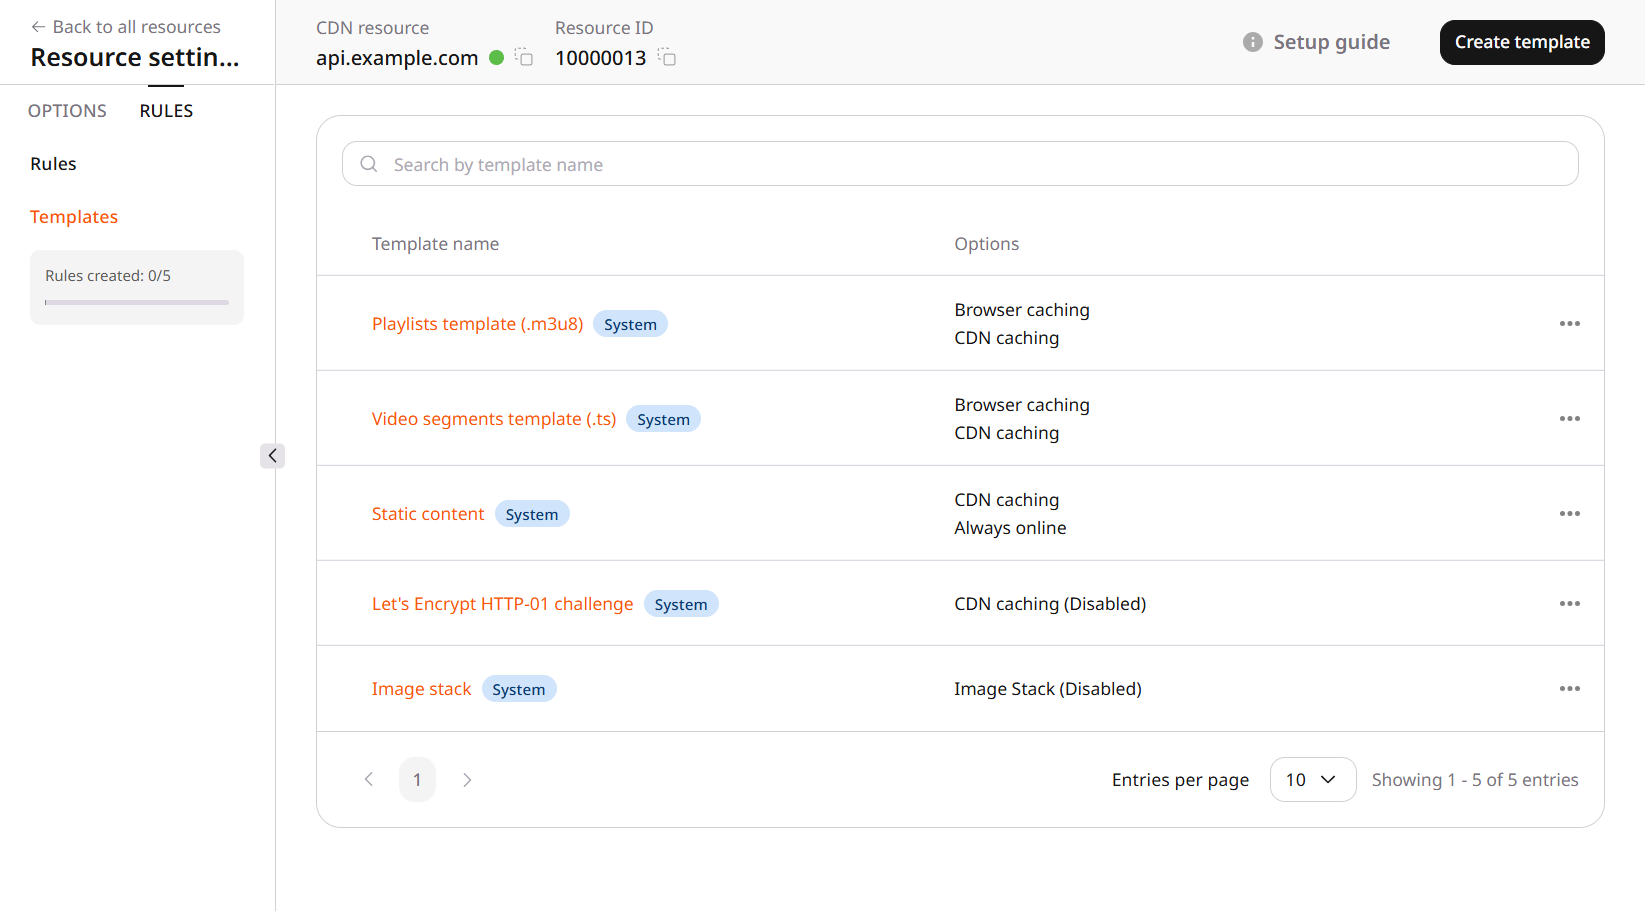
[Create rule](/cdn/cdn-resource-options/rules-for-particular-files/create-a-rule-manually-or-from-a-template-to-configure-settings-for-particular-files) starts blank or from a template. A template already holds a path, a pull protocol, and the options to override. [Rule templates](/cdn/cdn-resource-options/rules-for-particular-files/create-a-cdn-resource-rule-template-manually-or-use-a-system-one) include system presets for playlists, video segments, static content, the Let's Encrypt HTTP-01 challenge, and Image Stack. A system template opens as a read-only view of that preset.