

1
Open the server
- Virtual Machine
- Bare Metal
Log in to the Gcore Customer Portal and navigate to Cloud > Virtual Instances. Open the Virtual Machine.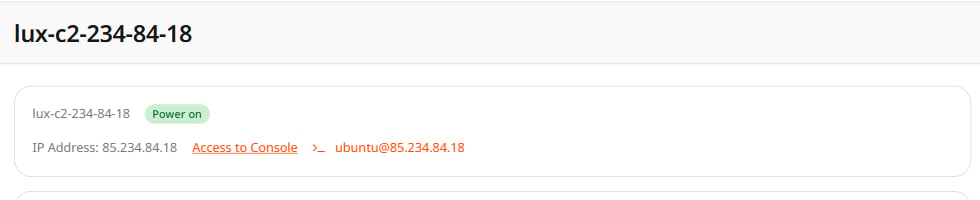
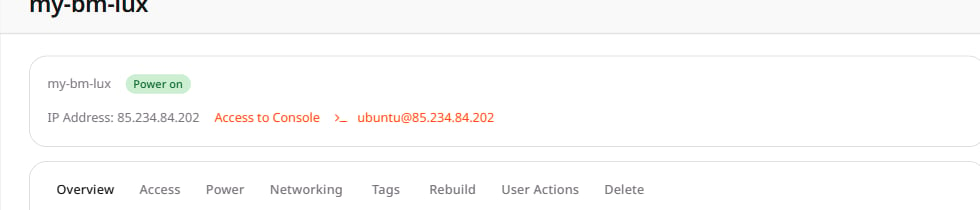
ubuntu.2
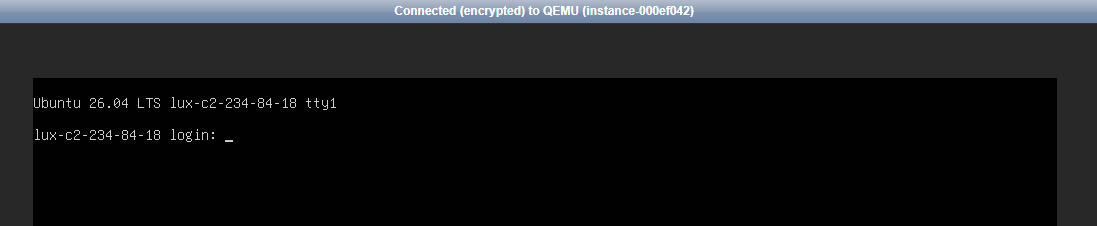
Open the console
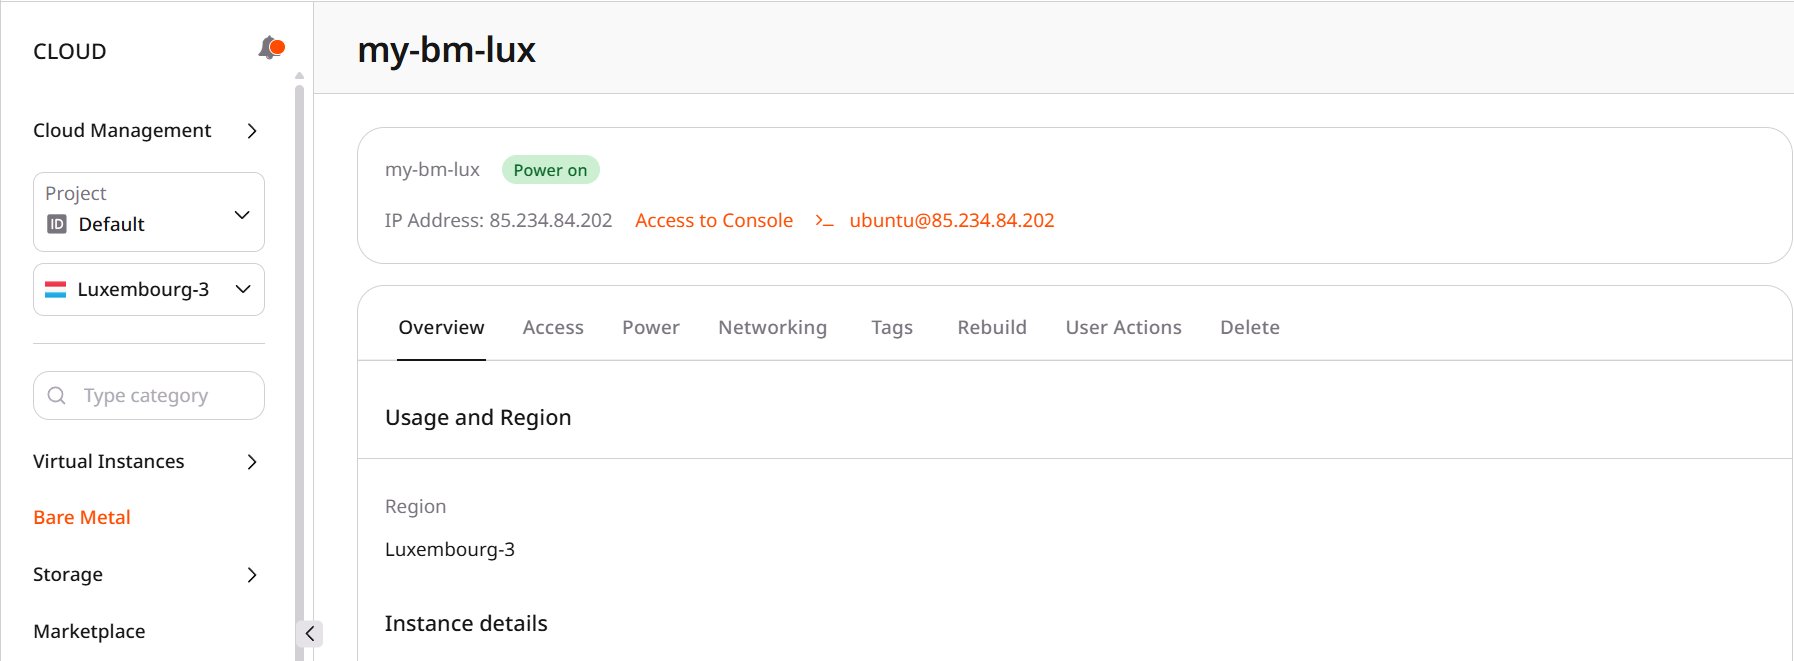
Not every Bare Metal platform provides Access to Console.
3
Open the GRUB menu
Open the boot menu before the login prompt: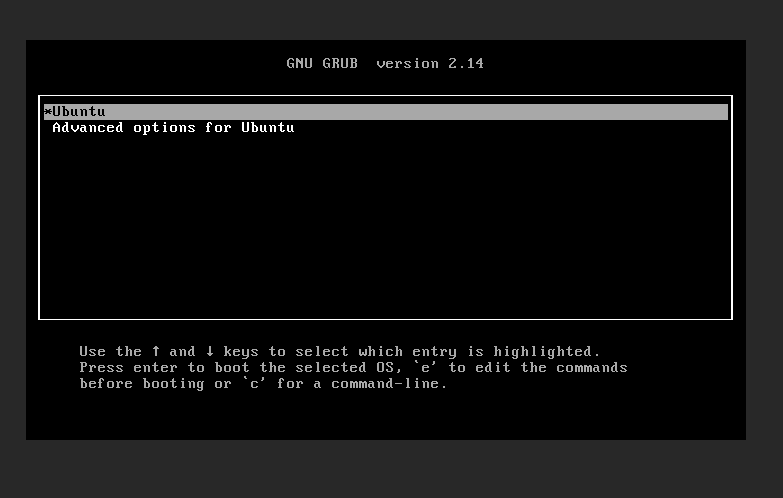
- Click the console screen so keystrokes reach the server.
- Click Send CtrlAltDel.
- Press Escape until GNU GRUB appears.
4
Boot recovery mode
On an Ubuntu cloud image, select Advanced options for Ubuntu and press Enter. Then select the entry that ends with 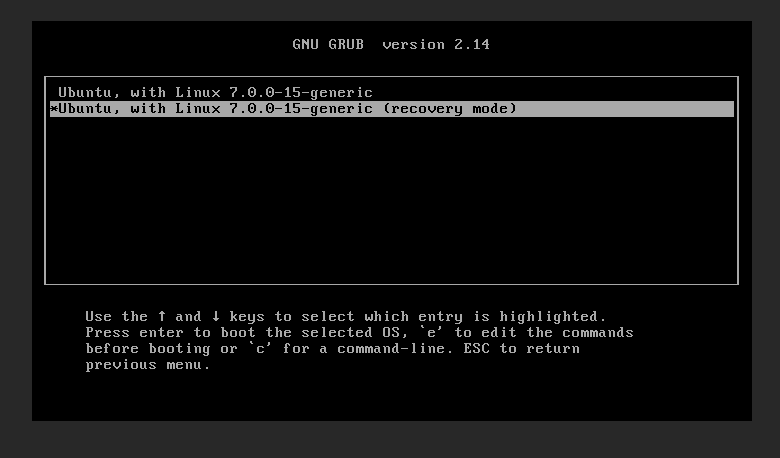
(recovery mode) and press Enter.5
Open a root shell
In Recovery Menu (filesystem state: read-only), select root (Drop to root shell prompt) and press Enter.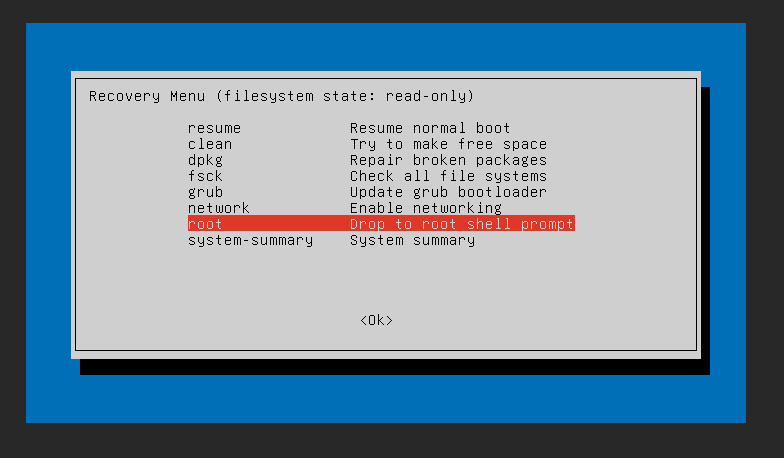
Press Enter for system maintenance (or press Control-D to continue):, press Enter. The menu frame can remain on screen after the shell starts, while the shell is active once a prompt ending in ~# appears at the bottom.Install a public key
Use this section when the server must accept a new SSH key. The root shell from the procedure above is already open.1
Remount the root filesystem
Recovery mounts the root filesystem read-only, so remount it before writing the key:When the command returns to the prompt without an error, the root filesystem accepts writes.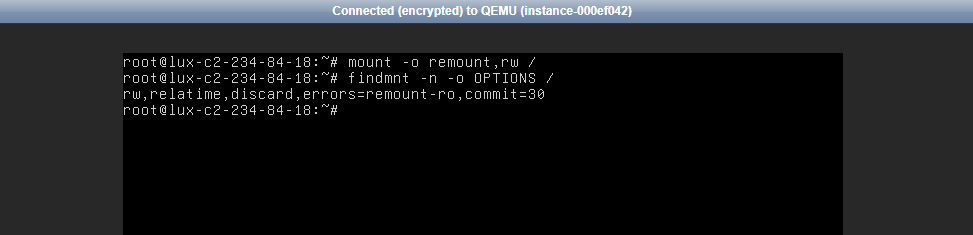
2
Install the public key
Write the new public key for the login beside Access to Console into Replace
authorized_keys on the local disk. On Ubuntu the file is /home/ubuntu/.ssh/authorized_keys, and when the login label names another account, use that account’s home directory.PUBLIC_KEY with the OpenSSH public key on one line.3
Set ownership and permissions
Set ownership and modes, then run Keep
sync before the reboot:/home/ubuntu at mode 750, because SSH succeeded with that mode on the Ubuntu image.4
Reboot the server
Reboot into the default GRUB entry:
5
Confirm SSH access
From a client that holds the matching private key, connect with the login from the server page:Replacing
authorized_keys makes the previous private key fail with Permission denied (publickey).